Skip to content

    The GCC practice · Dubai 25.20°N

    Governance, risk and compliance across the Gulf, led by a partner on the ground.

    Regulation in the GCC has moved from emerging to enforced, and it now reaches well beyond data. Boards answer to corporate governance codes, regulators expect a working compliance function, and supervisors look at third parties, resilience, data, security and AI together.

    We advise organisations in Saudi Arabia, the UAE, Qatar, Bahrain and Oman, and the European groups that operate there, from our Dubai office, with the same team that carries the European work.

    discuss a GCC engagement →

    § 01The rules we cover

    Country by country.

    The rules differ in detail and converge in intent. We design one governance and control framework and document where each regime genuinely diverges.

    01

    Saudi Arabia

    Governance and compliance: CMA Corporate Governance Regulations · SAMA rules and compliance function requirements · anti-money-laundering and counter-terrorist financing obligations · Competition Law

    Resilience and cyber: SAMA Cyber Security Framework and Business Continuity Management Framework · NCA Essential Cybersecurity Controls

    Data and AI: Personal Data Protection Law (PDPL) and implementing regulations · NDMO data governance · SDAIA AI Ethics Principles

    02

    UAE, federal

    Governance and compliance: SCA corporate governance rules for listed companies · CBUAE regulations and standards · anti-money-laundering law and sanctions obligations · Competition Law

    Resilience and cyber: UAE Information Assurance Standards · business continuity expectations of sector regulators

    Data and AI: Federal Decree-Law 45 of 2021 (PDPL) · Child Digital Safety Law · UAE Charter for AI

    03

    UAE, DIFC

    Governance and compliance: DFSA rulebook, including governance, systems and controls, and compliance and MLRO functions

    Data and AI: DIFC Data Protection Law 2020 · Regulation 10 on autonomous and semi-autonomous systems

    04

    UAE, ADGM

    Governance and compliance: FSRA rulebook, including governance, compliance and anti-money-laundering requirements

    Data: ADGM Data Protection Regulations 2021

    05

    Qatar

    Governance and compliance: QFMA Governance Code · QCB regulations · anti-money-laundering law

    Cyber and data: National Information Assurance standard · Personal Data Privacy Protection Law · QFC Data Protection Regulations

    06

    Bahrain

    Governance and compliance: Corporate Governance Code · CBB rulebook, including compliance, business continuity and cyber requirements

    Data: Personal Data Protection Law

    07

    Oman

    Governance and compliance: CMA Code of Corporate Governance · Central Bank of Oman requirements

    Data: Personal Data Protection Law and executive regulations

    § 03Who leads it
    01
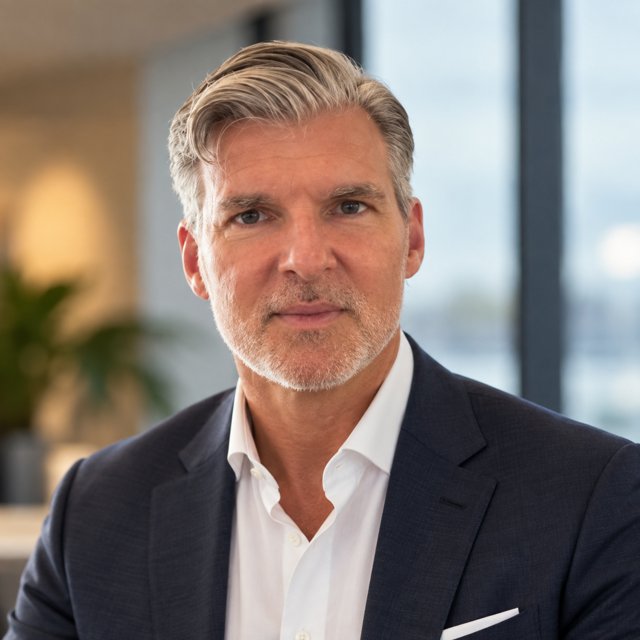
    Simon Leadbetter, Associate Partner, GCC, White Label Consultancy

    Associate Partner

    Simon Leadbetter

    Associate Partner, GCC

    Simon is a lawyer and digital trust, governance and transformation programme director with 20 years of GRC experience across the UK and the GCC, spanning data protection, AI governance and regulatory frameworks. Before joining WLC, he served six years as Director of Personal Data Protection at NEOM, where he led enterprise privacy governance and PDPL compliance and helped define NEOM's AI Ethics Council, after leading the development of a draft data protection law, regulation and operating model for a new Saudi regulator. He previously spent 20 years at Accenture across the UK and the UAE, including building its data privacy centre of excellence for GDPR. Simon holds the FIP, CIPP/E and CIPM certifications.

    Dubai office: +971 558 701 959, Dubai World Trade Center, Sheikh Zayed Road. Meet the full team.